
Enable data collection for NetScaler Gateway appliances deployed in single-hop mode
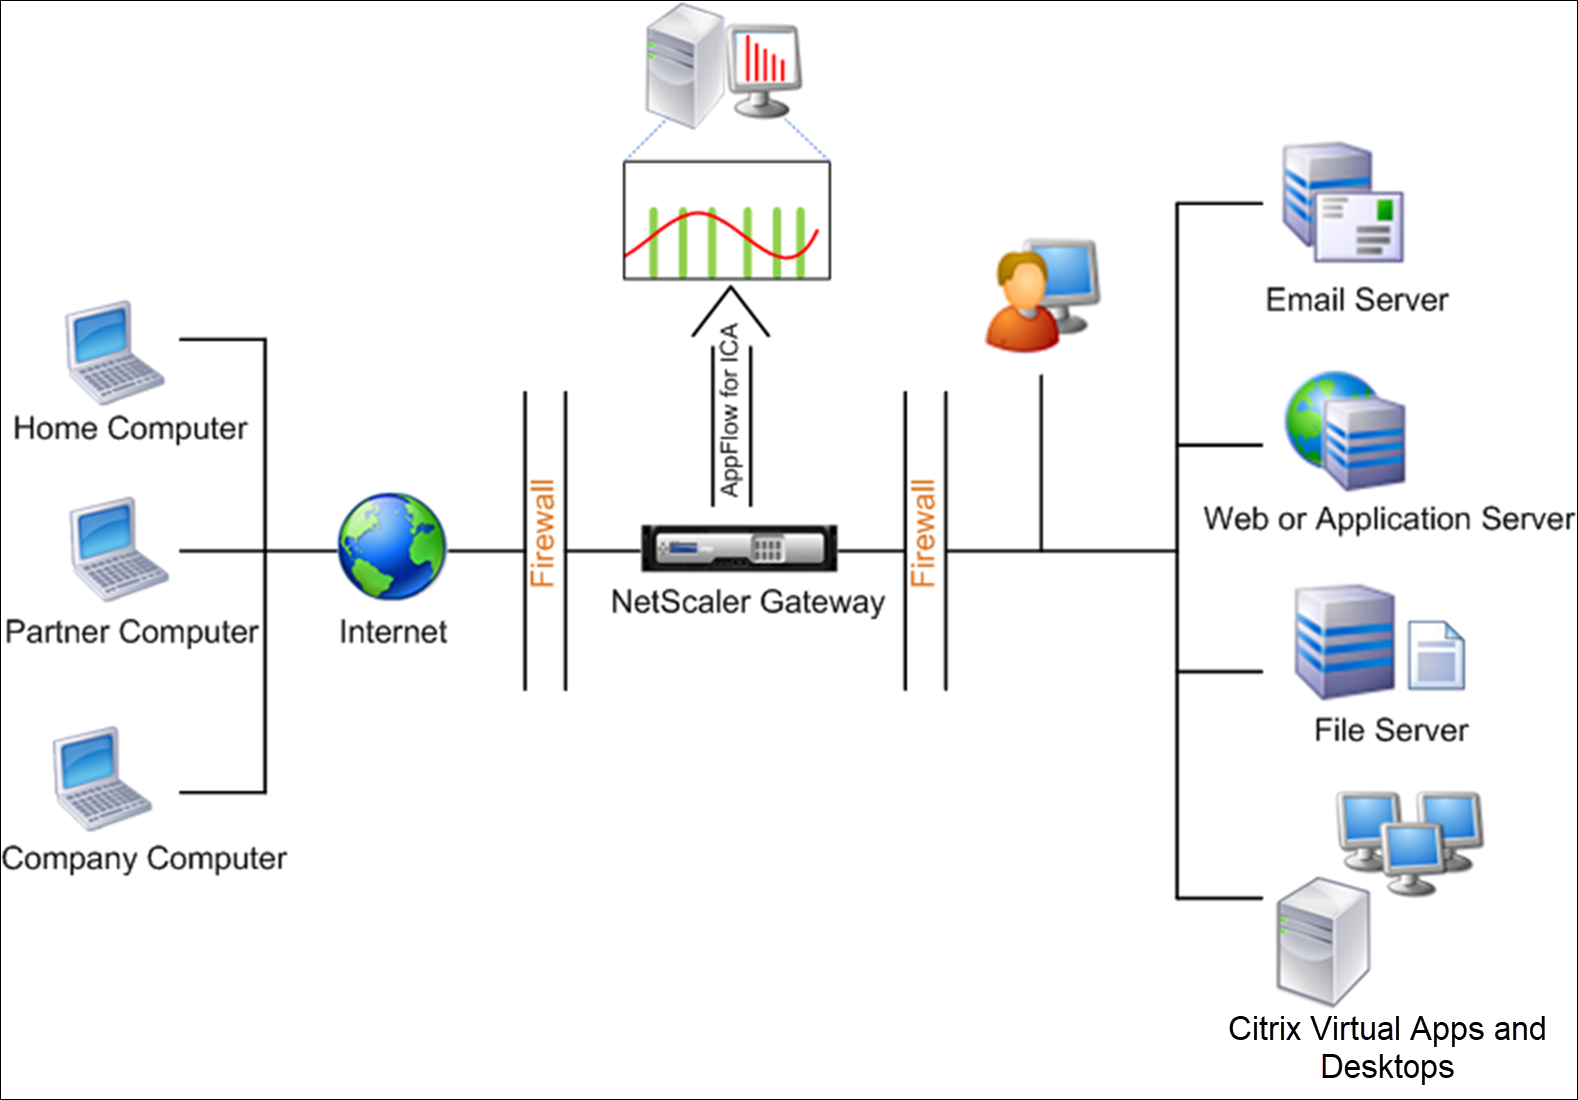
When NetScaler Gateway is deployed in single-hop mode, the NetScaler Gateway is at the edge of the network and proxies ICA connections to the desktop delivery infrastructure. This deployment is the simplest and most common deployment. This mode provides security if an external user tries to access the internal network in an organization. In single-hop mode, users access the NetScaler appliances through a virtual private network (VPN).
To start collecting the reports, you must add the NetScaler Gateway appliance to the NetScaler Console inventory and enable AppFlow on NetScaler Console. The following image illustrates a NetScaler Console deployed in single-hop mode
Related information
Enable the AppFlow feature from NetScaler Console
-
Navigate to Infrastructure > Instances, and select the NetScaler instance you want to enable analytics.
-
From the Select Action list, select Configure Analytics.
-
Select the VPN virtual servers, and click Enable Analytics.
-
Select Web Insight.
-
Click OK.
Note
The following commands start to run in the background when you enable AppFlow® in single-hop mode. These commands are explicitly specified here for troubleshooting purposes.
-
add appflow collector \<name\> -IPAddress \<ip\_addr\> -
add appflow action \<name\> -collectors \<string\> -
set appflow param -flowRecordInterval \<secs\> -
disable ns feature AppFlow -
enable ns feature AppFlow -
add appflow policy \<name\> \<rule\> \<expression\> -
set appflow policy \<name\> -rule \<expression\> -
bind vpn vserver \<vsname\> -policy \<string\> -type \<type\> >-priority \<positive\_integer\> -
set vpn vserver \<name\> -appflowLog ENABLED -
save ns config