
Kubernetes Ingress solution
This topic provides an overview of the Kubernetes Ingress solution provided by NetScaler® and explains the benefits.
Related information
What is Kubernetes Ingress?
When you are running an application inside a Kubernetes cluster, you need to provide a way for external users to access the applications from outside the Kubernetes cluster. Kubernetes provides an object called Ingress that provides the most effective way to expose multiple services using a stable IP address. A Kubernetes ingress object is always associated with one or more services and acts as a single-entry point for external users to access services running inside the cluster.
The following diagram explains how Kubernetes Ingress works. 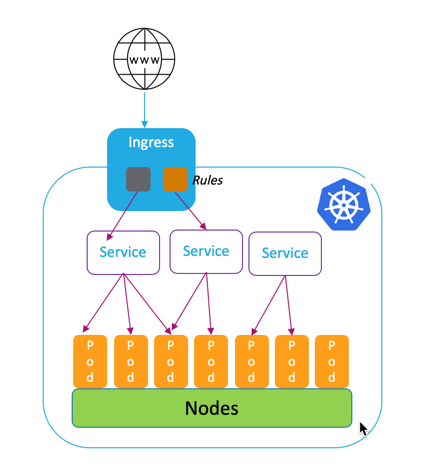
Kubernetes Ingress implementation consists of the following components:
-
Ingress resource. An Ingress resource allows you to define rules for accessing the applications from outside of the cluster.
-
Ingress controller. An Ingress controller is an application deployed inside the cluster that interprets rules defined in the Ingress. Ingress controller converts the Ingress rules into configuration instructions for a load balancing application integrated with the cluster. The load balancer can be a software application running inside your Kubernetes cluster or a hardware appliance running outside the cluster.
-
Ingress device. An Ingress device is a load balancing application like NetScaler CPX, VPX, or MPX which performs load balancing according to the configuration instructions provided by the Ingress controller.
What is the Kubernetes Ingress solution from NetScaler?
In this solution, NetScaler provides an implementation of Kubernetes Ingress controller to manage and route traffic into your Kubernetes cluster using NetScaler ADCs (NetScaler CPX, VPX, or MPX). The NetScaler Ingress Controller integrates NetScaler ADCs with your Kubernetes environment and configures NetScaler CPX, VPX, or MPX according to the Ingress rules.
Standard Kubernetes Ingress solutions provide load balancing only at layer 7 (HTTP or HTTPS traffic). Some times, you need to expose many legacy applications which rely on TCP or UDP or applications and need a way to load balance those applications. NetScaler Ingress Controller solution provides TCP, TCP-SSL, and UDP traffic support apart from the standard HTTP or HTTPS Ingress. Also, it works seamlessly across multiple clouds or on-premises data centers.
NetScaler provides enterprise-grade traffic management policies like rewrite and responder policies for efficiently load balancing traffic at layer 7. However, Kubernetes Ingress lacks such enterprise-grade traffic management policies. With the Kubernetes Ingress solution from NetScaler, you can apply rewrite and responder policies for application traffic in a Kubernetes environment using CRDs provided by NetScaler.
The Kubernetes Ingress solution from NetScaler also supports automated canary deployment for your CI/CD application pipeline. In this solution, NetScaler is integrated with the Spinnaker platform and acts as a source for providing accurate metrics for analyzing Canary deployment using Kayenta. After analyzing the metrics, Kayenta generates an aggregate score for the canary and decides to promote or fail the Canary version. You can also regulate traffic distribution to the Canary version using the NetScaler policy infrastructure.
The following table summarizes the benefits offered by the Ingress solution from NetScaler over Kubernetes Ingress.
| Features | Kubernetes Ingress | Ingress Solution from NetScaler |
|---|---|---|
| HTTP and HTTPs support | Yes | Yes |
| URL routing | Yes | Yes |
| TLS | Yes | Yes |
| Load balancing | Yes | Yes |
| TCP, TCP-SSL | No | Yes |
| UDP | No | Yes |
| HTTP/2 | Yes | Yes |
| Automated canary deployment support with CI/CD tools | No | Yes |
| Support for applying NetScaler rewrite and responder policies | No | Yes |
| Authentication (Open Authorization (OAuth), mutual TLS (mTLS)) | No | Yes |
| Support for applying NetScaler Rate Limiting policies | No | Yes |
Deployment options for Kubernetes Ingress solution
Kubernetes Ingress solution from NetScaler provides you flexible architecture depending on how you want to manage your NetScaler ADCs and Kubernetes environment.
Unified Ingress (single-tier)
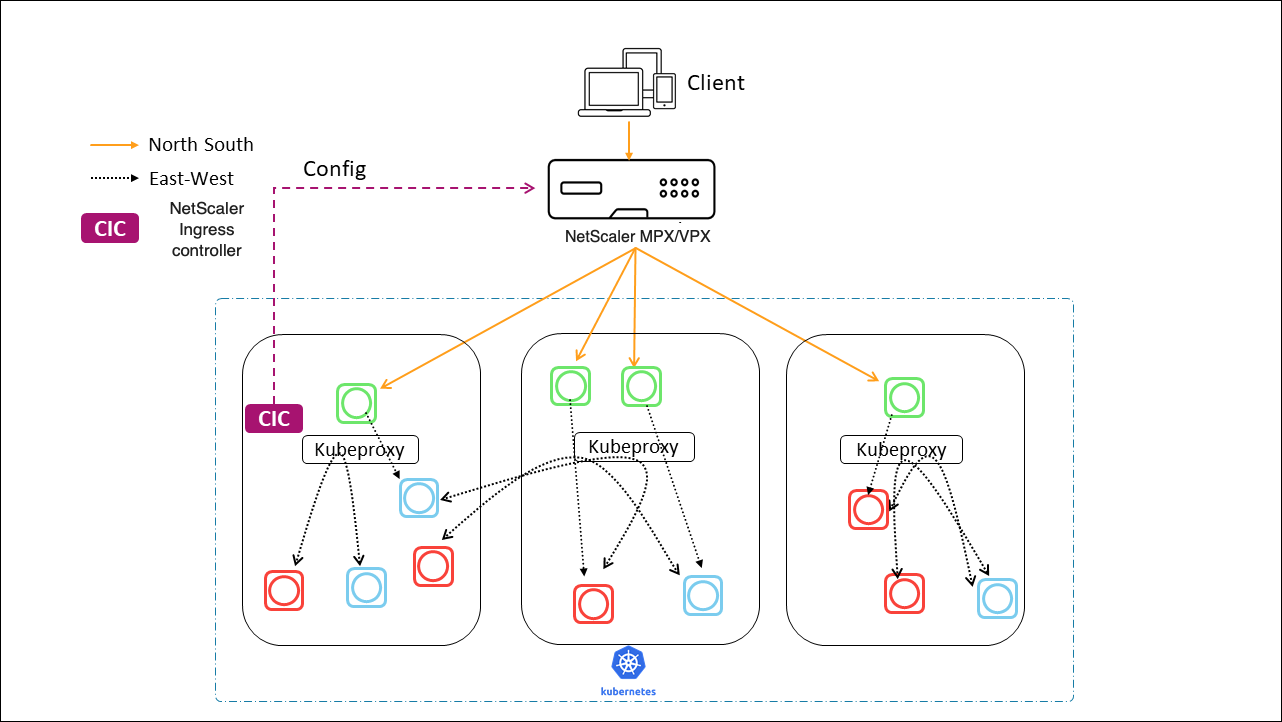
In a unified Ingress (single-tier) architecture, a NetScaler MPX or VPX device deployed outside the Kubernetes cluster is integrated with the Kubernetes environment using the NetScaler Ingress Controller. The NetScaler Ingress Controller is deployed as a pod in the Kubernetes cluster and automates the configuration of NetScaler ADCs based on changes to the microservices or the Ingress resources. The NetScaler device performs functions like load balancing, TLS termination, and HTTP or TCP protocol optimizations on inbound traffic and then routes the traffic to the correct microservice within a Kubernetes cluster. This architecture suits best in scenarios where the same team manages the Kubernetes platform and other networking infrastructure including application delivery controllers (ADCs).
The following diagram shows a deployment using the unified Ingress architecture.
A unified Ingress solution provides the following key benefits:
-
Provides a way to extend the capabilities of your existing NetScaler infrastructure to the Kubernetes environment
-
Enables you to apply traffic management policies for inbound traffic
-
Provides a simplified architecture suitable for network-savvy DevOps teams
-
Supports multitenancy
Dual-tier Ingress
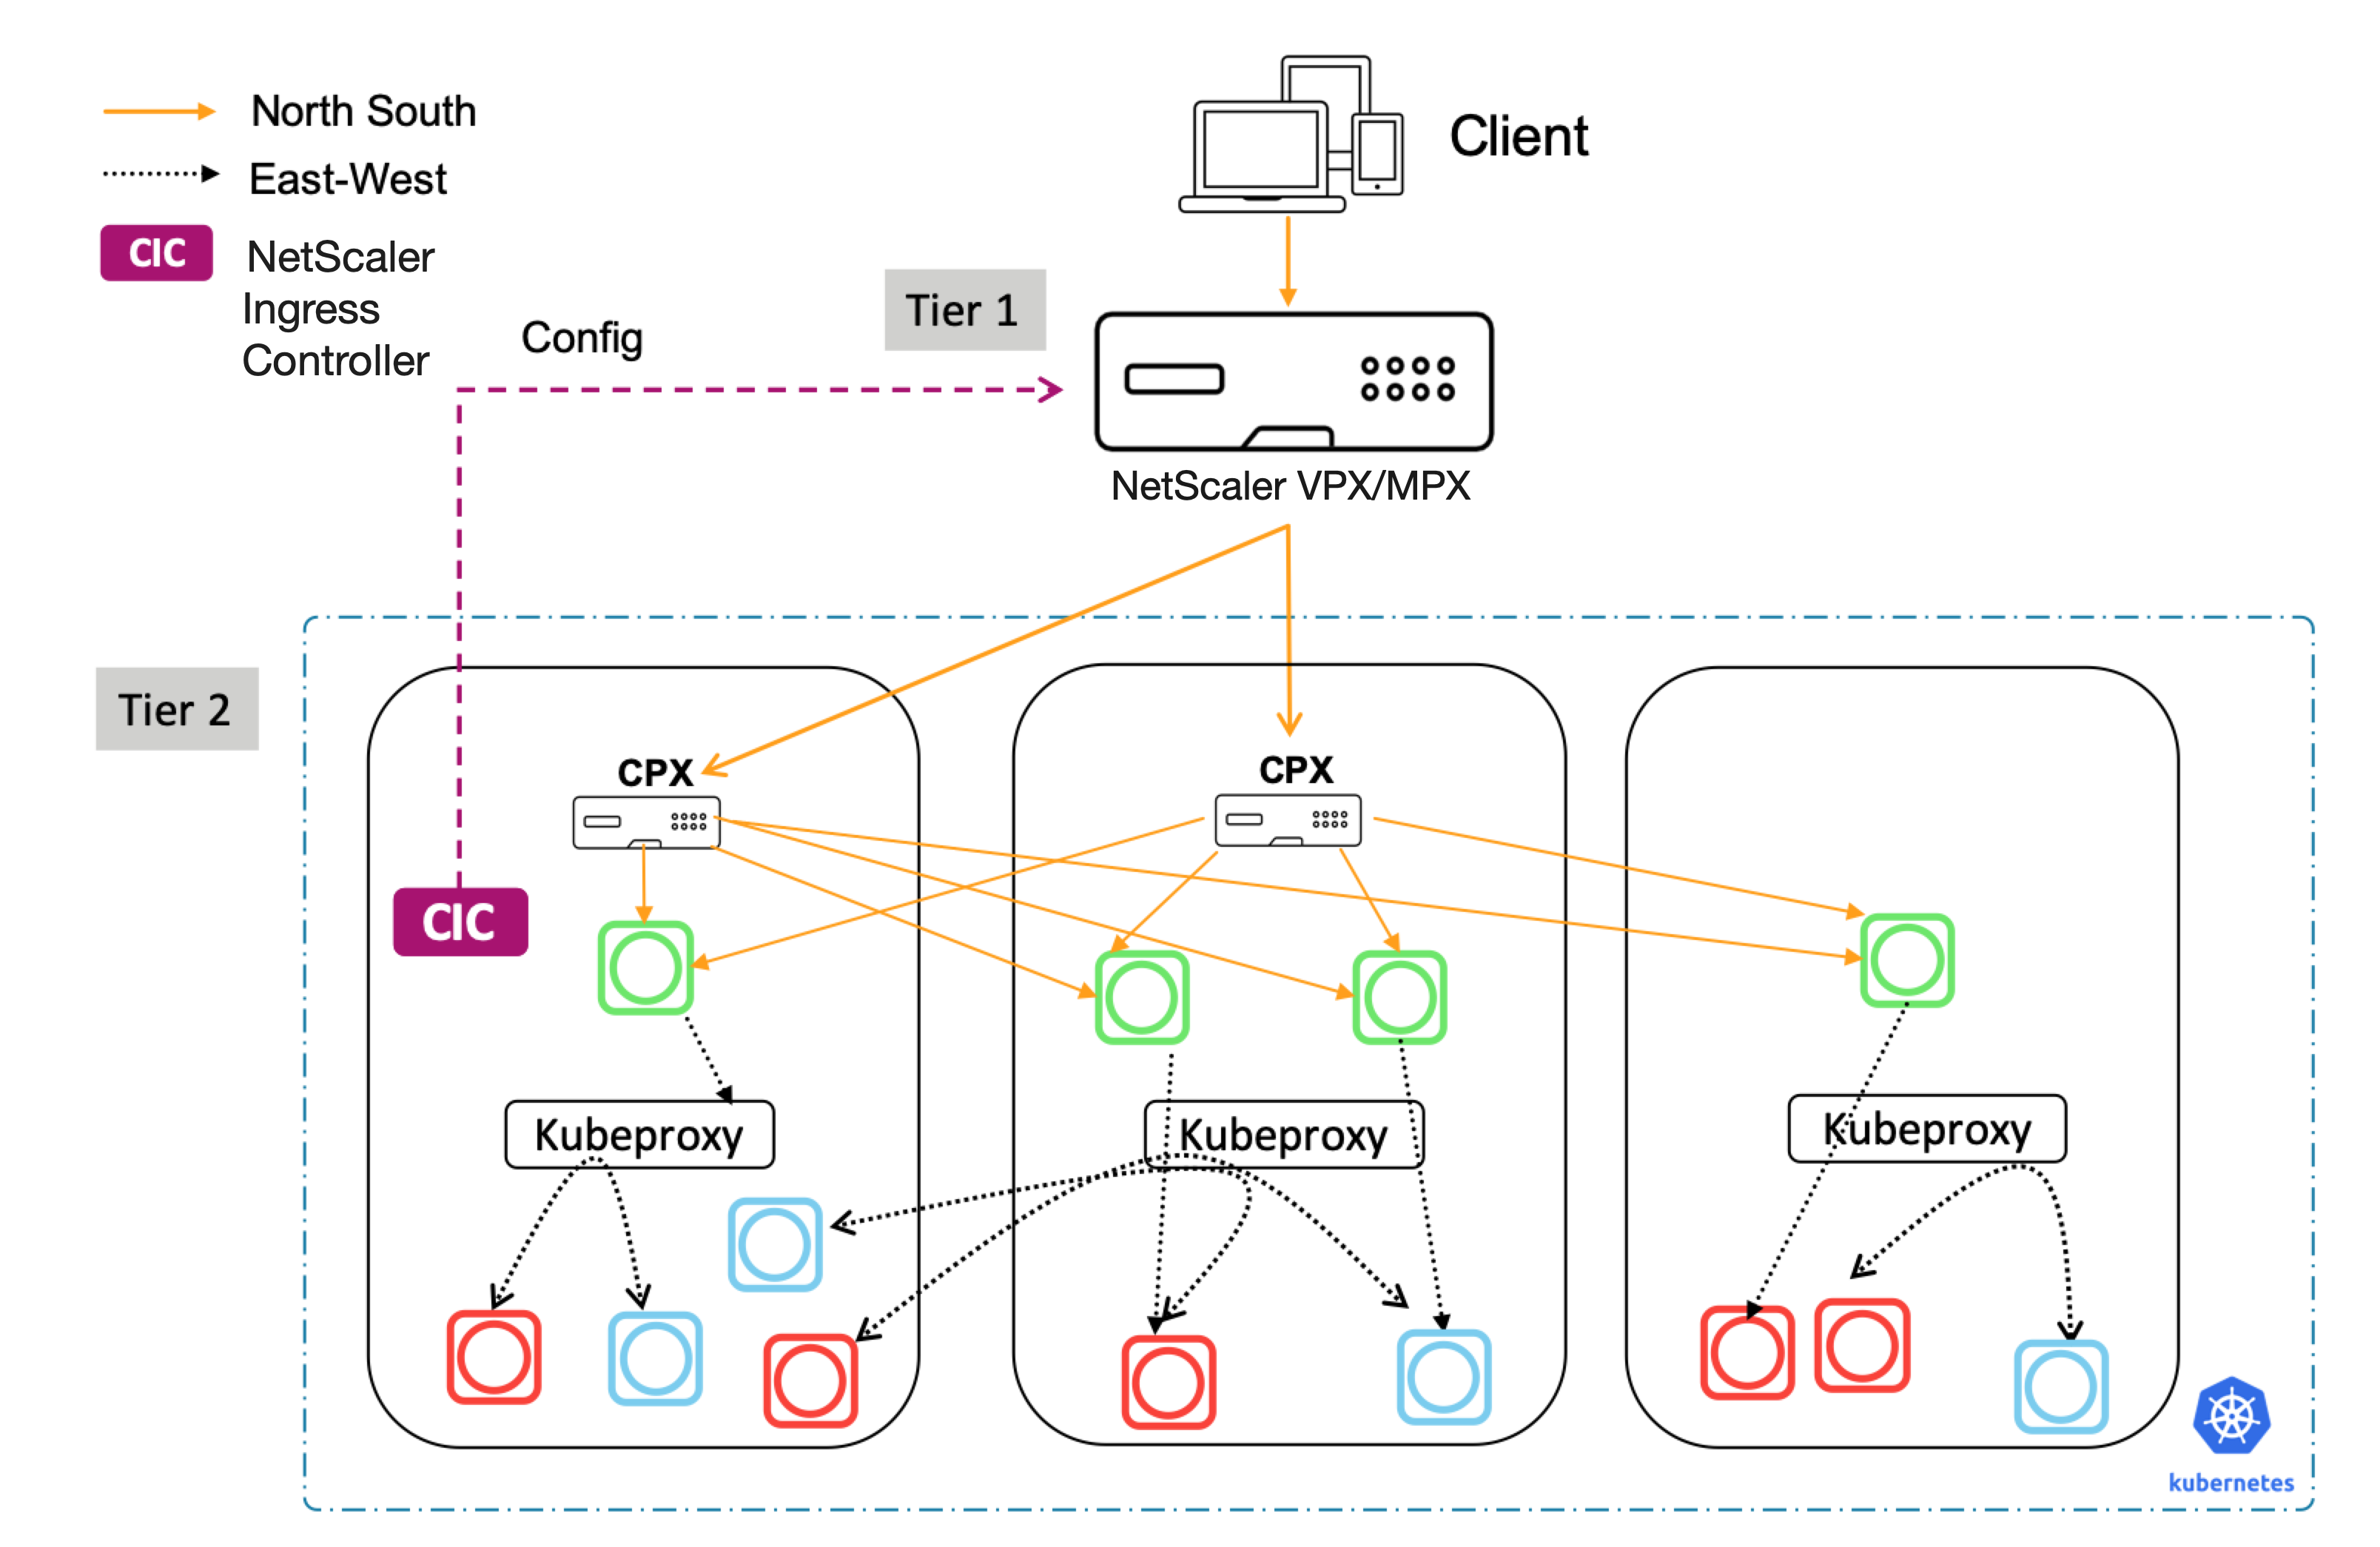
In a dual-tier architecture, NetScaler (MPX or VPX) deployed outside the Kubernetes cluster acts at tier 1 and load balances North-South traffic to NetScaler CPXs running inside the cluster. NetScaler CPX acts at tier 2 and performs load balancing for microservices inside the Kubernetes cluster.
In scenarios where separate teams manage the Kubernetes platform and the network infrastructure, the dual-tier architecture is most suitable.
Networking teams use tier 1 NetScaler for use cases such as GSLB, TLS termination on the hardware platform, and TCP load balancing. Kubernetes platform teams can use tier 2 NetScaler (CPX) for Layer 7 (HTTP/HTTPS) load balancing, mutual TLS, and observability or monitoring of microservices. The tier 2 NetScaler (CPX) can have a different software release version than the tier 1 NetScaler to accommodate newly available capabilities.
The following diagram shows a deployment with dual-tier architecture.
A dual-tier Ingress provides the following key benefits:
-
Ensures high velocity of application development for developers or platform teams
-
Enables applying developer driven traffic management policies for microservices inside the Kubernetes cluster
-
Enables cloud scale and multitenancy
For more information, see the NetScaler Ingress Controller documentation.