
Security Advisory (Preview)
Note:
Starting from 13.1-53.22 build, Security Advisory is automatically enabled. For more information, see Security Advisory
A safe, secure, and resilient infrastructure is the lifeline of any organization. Organizations must track new Common Vulnerabilities and Exposures (CVEs), and assess the impact of CVEs on their infrastructure. They must also understand and plan the mitigation and remediation to resolve the vulnerabilities.
NetScaler® ADM on-premises Security Advisory only highlights the NetScaler CVEs and the ADC instances that are at risk.
IMPORTANT
For a detailed analysis on the CVE impact, conclusive information on custom scans/system scans, remediation and mitigation workflows, try NetScaler ADM Service.
Related information
View security advisory
To access Security Advisory, navigate to Infrastructure > Instance Advisory > Security Advisory. You can see the vulnerability status of all the ADC instances that you manage through NetScaler ADM.
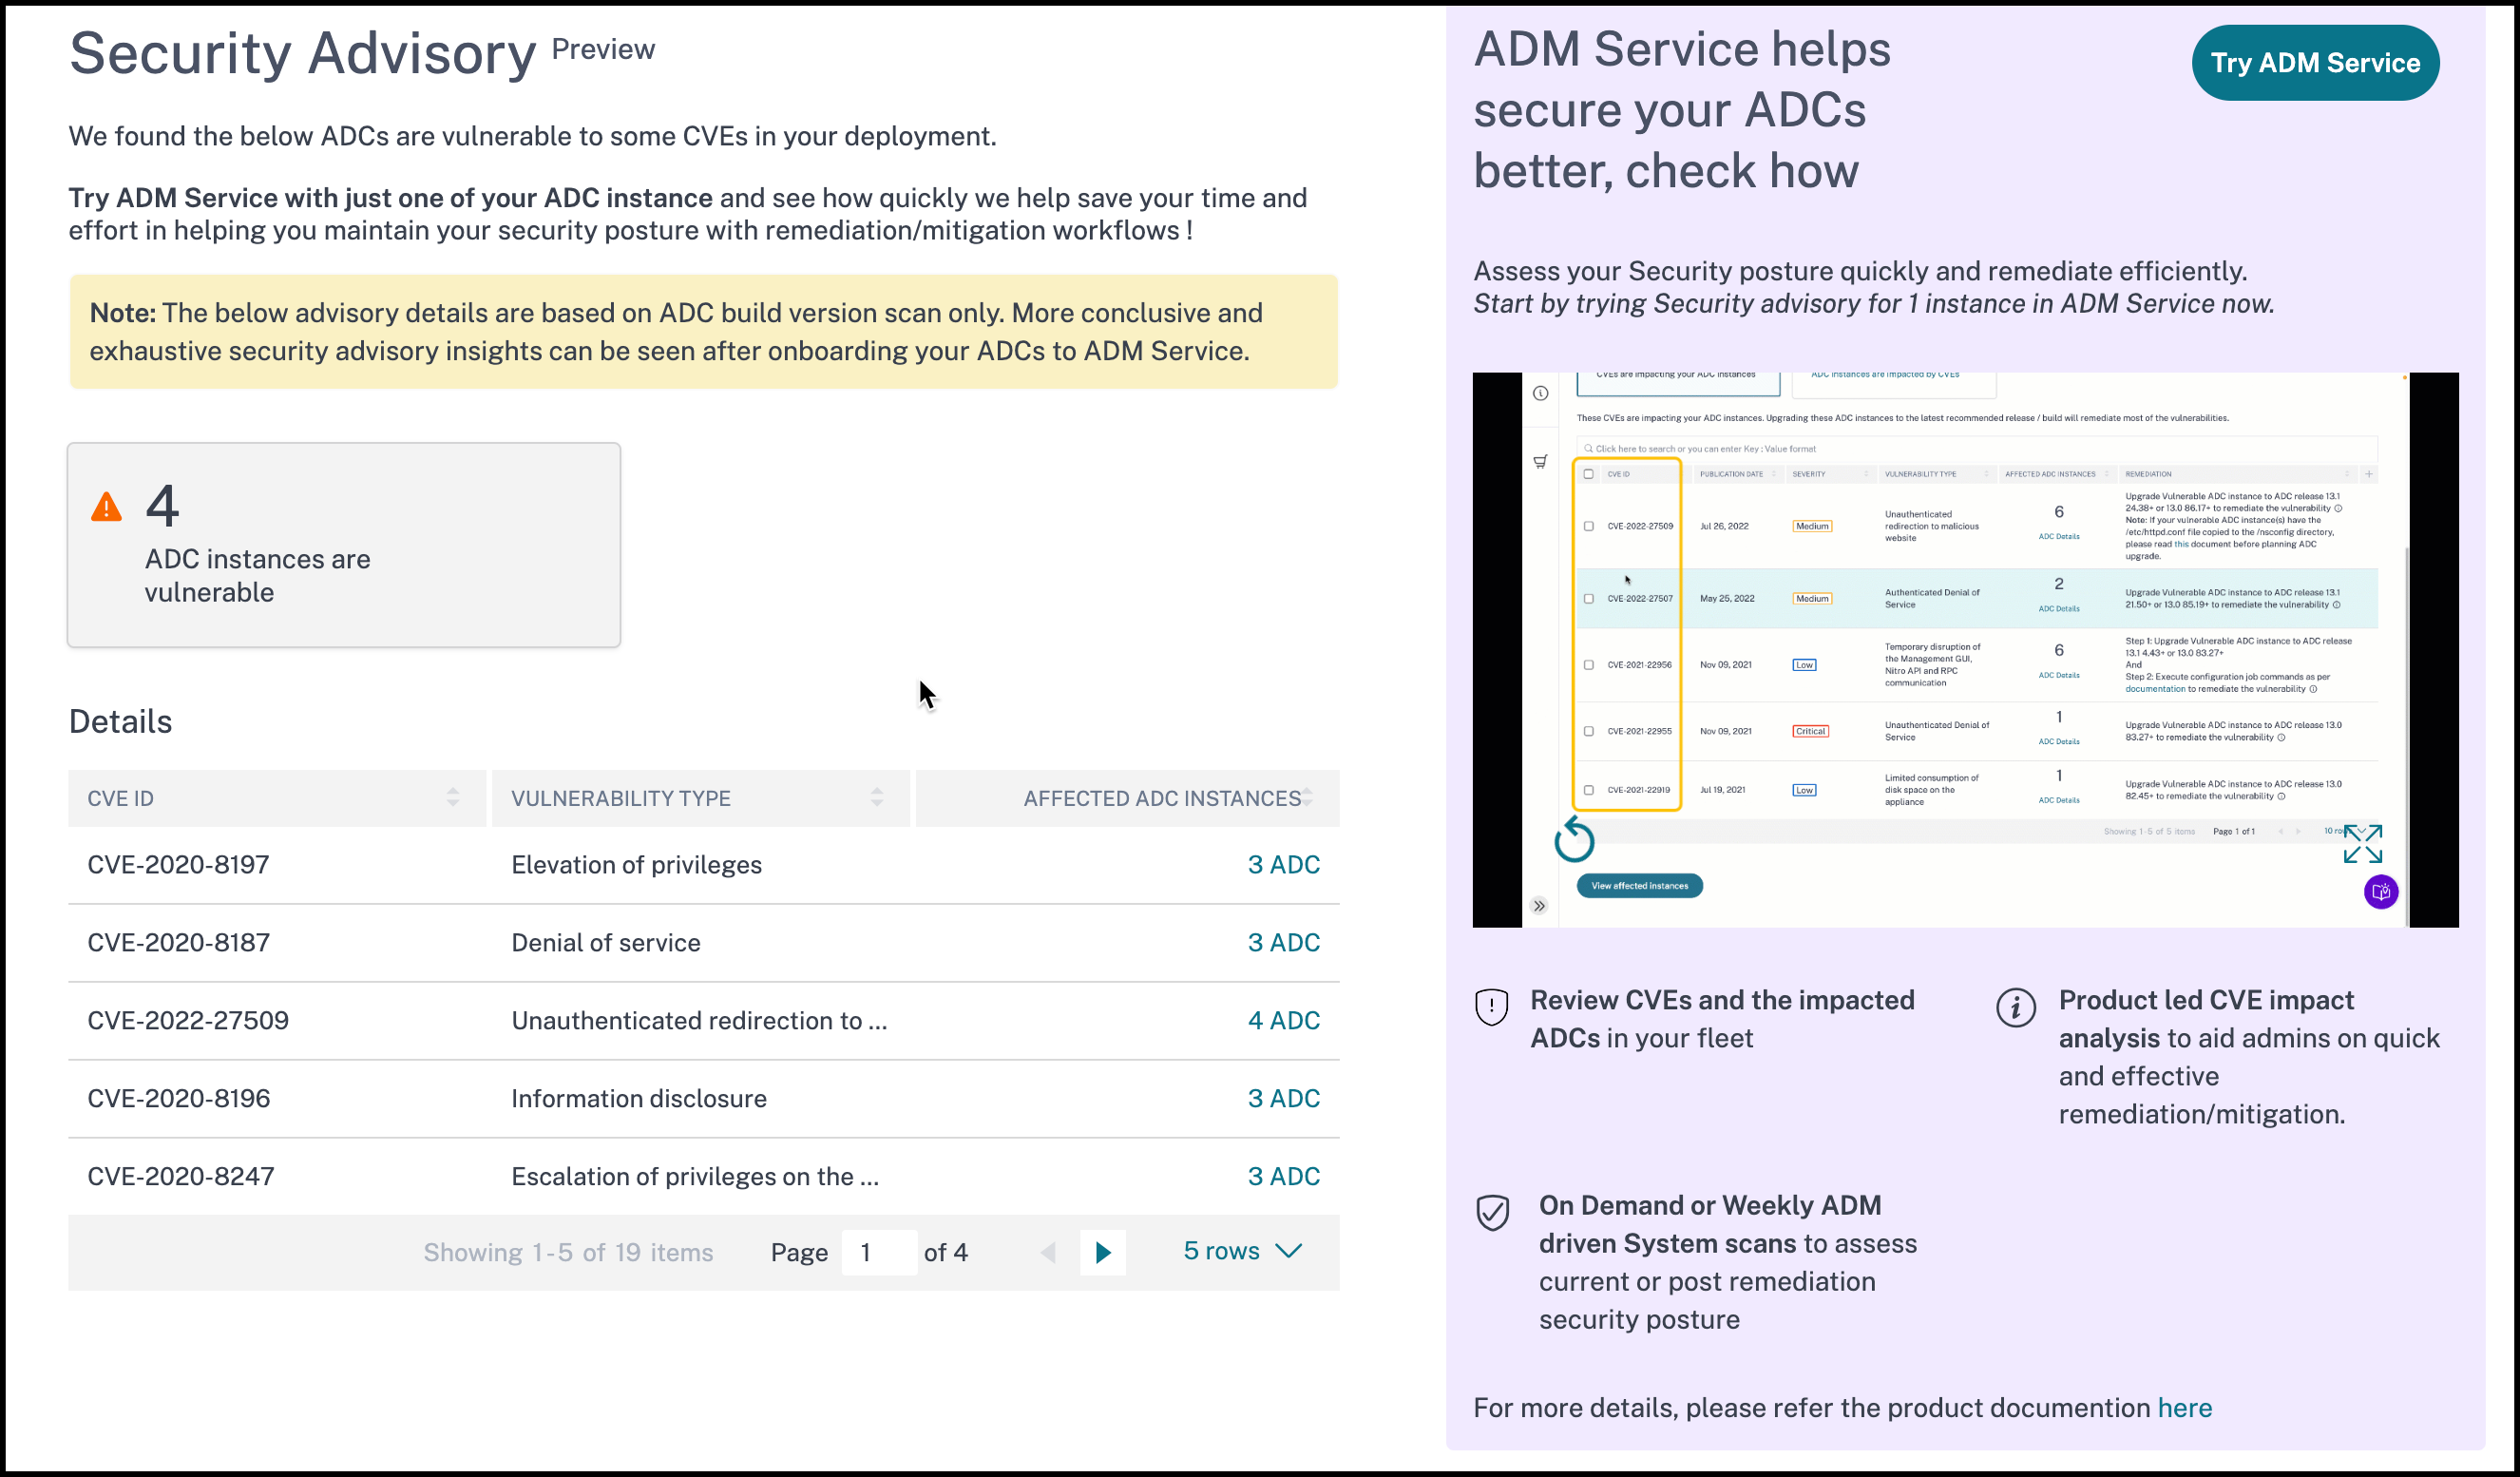
NetScaler ADM on-premises Security Advisory performs only ADC Version scan to check for CVEs and following information is displayed.
-
CVE ID: The ID of the CVE impacting the instances.
-
Vulnerability type: The type of vulnerability for this CVE.
-
Affected ADC instances: The instance count that the CVE ID is impacting.
NetScaler ADM on-premises Security Advisory also allows you to select one of the ADC instances, and onboard the ADC instance to ADM Service. Click Try ADM Service and onboard the ADC instance to ADM Service. ADM Service Security Advisory allows you to check the vulnerability type of a particular CVE and get information on mitigation and remediation to resolve the vulnerability.
For more information on the ADM Service Security Advisory, view the gif animation on the Security Advisory page.