
Authentication
Users can be authenticated either internally by NetScaler® ADM, externally by an authenticating server, or both. If local authentication is used, the user must be in the NetScaler ADM security database. If the user is authenticated externally, the user “external name” must match the external user identity registered with the authenticating server, depending on the selected authentication protocol.
NetScaler ADM supports external authentication by RADIUS, LDAP, and TACACS servers. This unified support provides a common interface to authenticate and authorize all the local and external Authentication, Authorization, and Accounting server users who are accessing the system. NetScaler ADM can authenticate users regardless of the actual protocols they use to communicate with the system. When a user attempts to access a NetScaler ADM implementation that is configured for external authentication, the requested application server sends the user name and password to the RADIUS, LDAP, or TACACS server for authentication. If the authentication is successful, the user is granted access to NetScaler ADM.
External authentication servers
NetScaler ADM sends all authentication, authorization, and auditing service requests to the remote RADIUS, LDAP, or TACACS server. The remote authentication, authorization, and auditing server receive the request, validates the request, and sends a response to NetScaler ADM. When configured to use a remote RADIUS, TACACS, or LDAP server for authentication, NetScaler ADM becomes a RADIUS, TACACS, or LDAP client. In any of these configurations, authentication records are stored in the remote host server database. The account name, assigned permissions, and time-accounting records are also stored on the authentication, authorization, and auditing server for each user.
Also, you can use the internal database of NetScaler ADM to authenticate users locally. You create entries in the database for users and their passwords and default roles. You can also select the authentication order for specific types of authentication. The list of servers in a server group is an ordered list. The first server in the list is always used unless it is unavailable, in which case the next server in the list is used. You can configure servers to include the internal database as a fallback authentication backup to the configured list of authentication, authorization, and auditing servers.
Authenticate users in NetScaler ADM
You can authenticate your users in NetScaler ADM in two ways:
-
Local users configured in NetScaler ADM
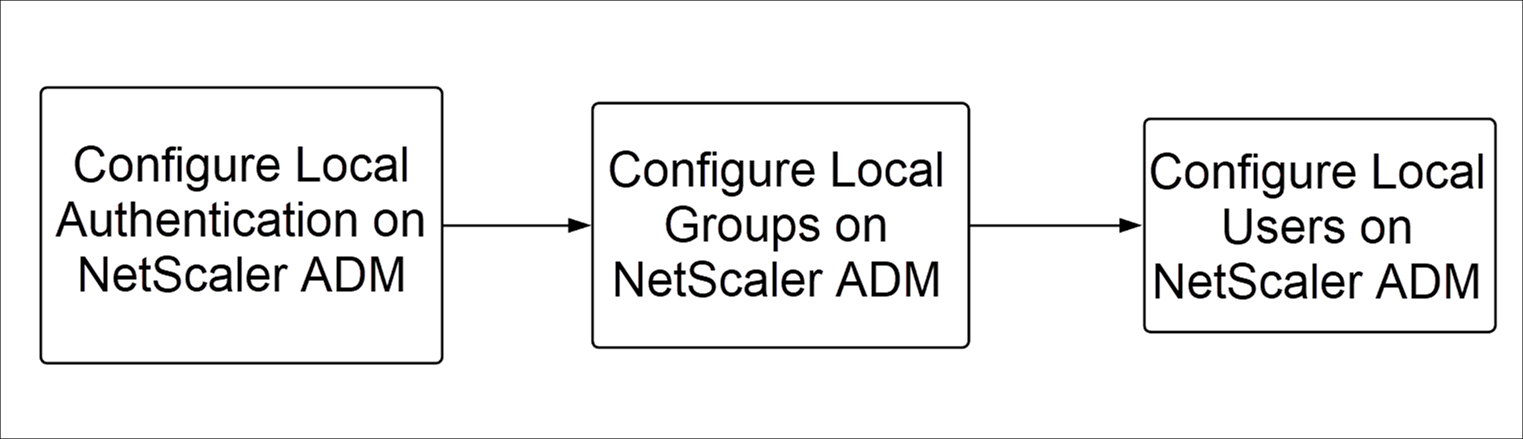 After configuration, the following is the workflow for user authentication in the local server.
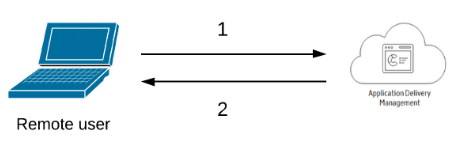 1 – The user logs on to NetScaler ADM2 – NetScaler ADM prompts the users for credentials for authentication and checks if the credentials match in the ADM database.
-
Using external authentication servers
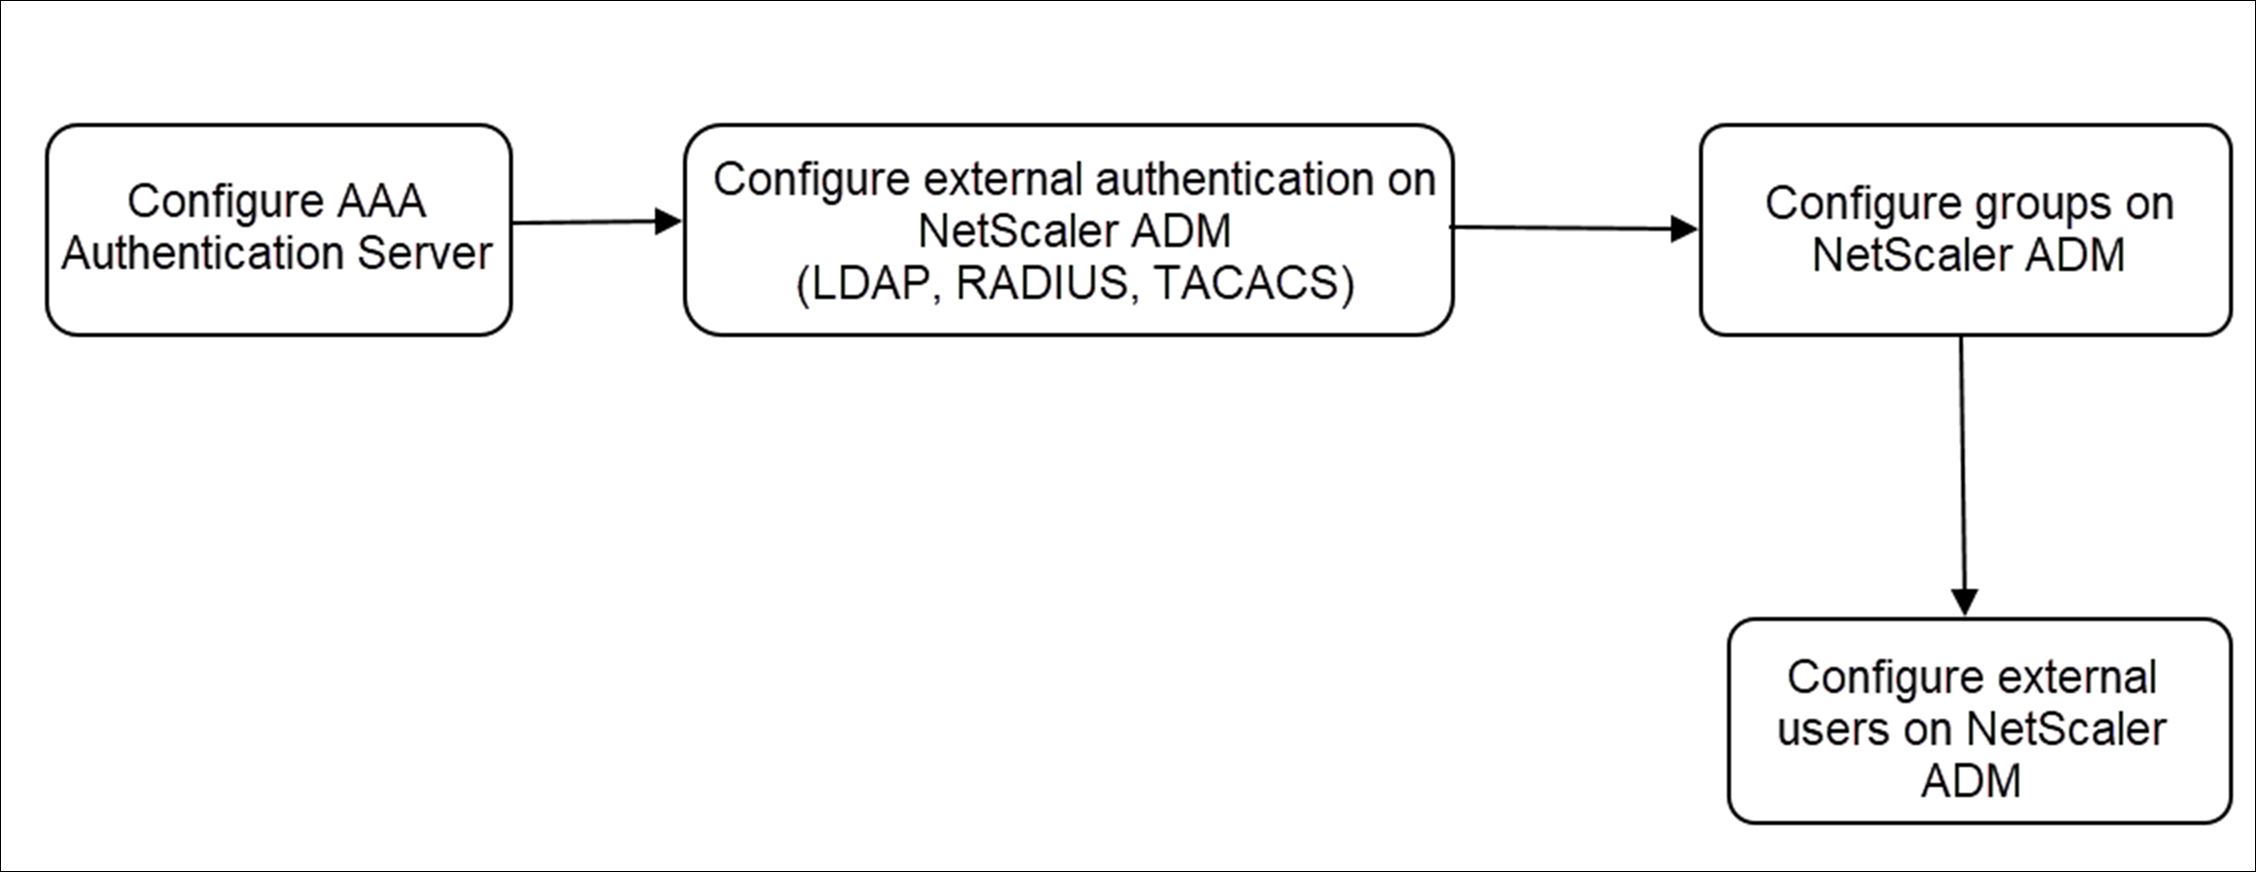 After configuration, the following is the workflow for user authentication in the external authentication, authorization, and auditing server:
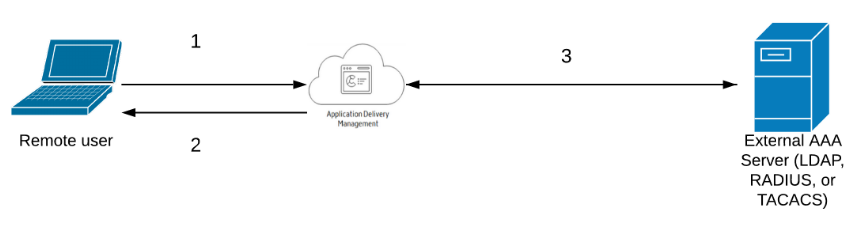 1 – The user connects with NetScaler ADM2 – NetScaler ADM prompts the user for credentials3 – NetScaler ADM validates the user credentials with the external authentication, authorization, and auditing server. If the validation is successful, the user can continue to log on