
Integrate NetScaler Gateway with StoreFront
This article describes how to create a NetScaler Gateway virtual server for remotely accessing StoreFront, for users who are using Citrix Workspace app or a web browser.
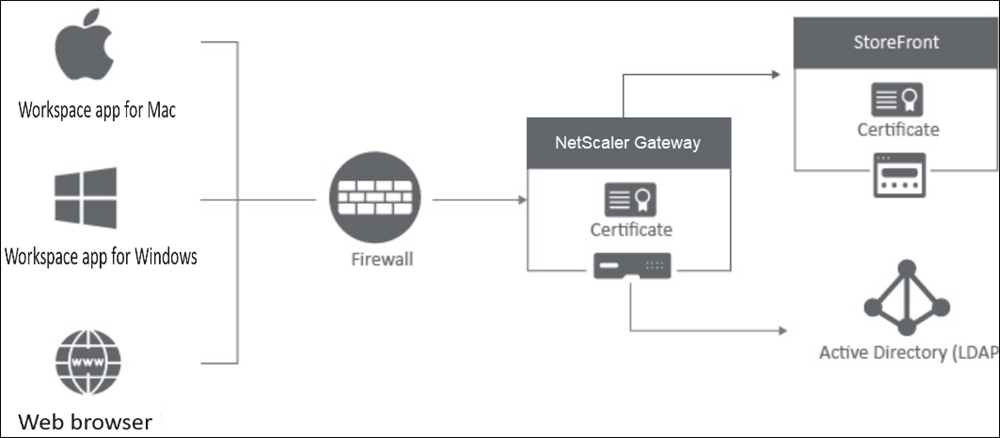
Users connect to NetScaler Gateway through a web browser or Citrix Workspace app. NetScaler Gateway authenticates users based on the configured policies. If the authentication is successful, then NetScaler Gateway enables the users to single sign-on to the store and proxies the StoreFront store to the user.
Important:
We recommend that you do not use the Citrix Virtual Apps and Desktops wizard to integrate NetScaler Gateway with StoreFront as it creates an invalid configuration by using the classic authentication policies (deprecated).
Configure NetScaler Gateway to use with StoreFront
To integrate NetScaler Gateway with StoreFront, complete the following steps:

1. Create a session policy for web browser-based access
-
Navigate to Configuration > NetScaler Gateway > Policies > Session.
-
In the Session Profiles tab, click Add.
-
Assign a name to the session profile.
-
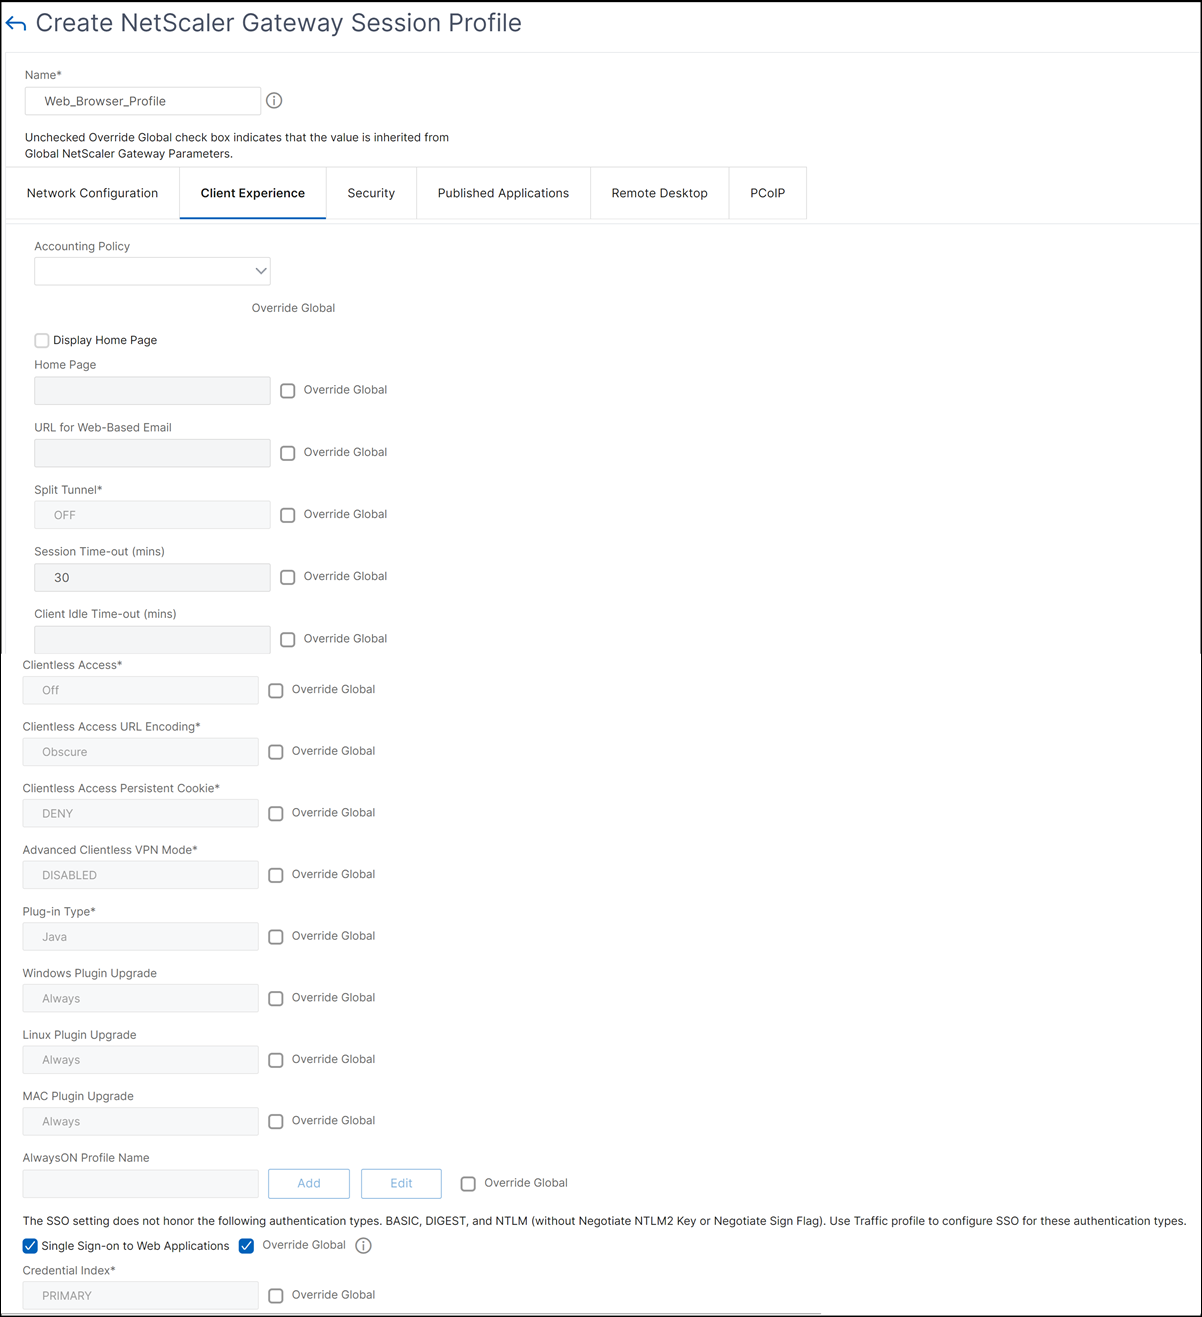
In the Client Experience tab, configure the following settings:
-
Session Time-out (mins): Set this to the desired inactivity timeout. This should be set to the same or lower than the web inactivity timeout configured in StoreFront for the store website. It is recommended that you select Override Global even if you intend to use the global session timeout settings. Failing to explicitly override this setting, even when using the default 30-minute timeout, can lead to authentication loops and force users to re-login.
-
Plug-in Type: To disable use of the Secure Access client, which is required to establish a full VPN, set this to Java. If you want to allow a full VPN, see Full VPN setup on NetScaler Gateway.
-
Single Sign-on to Web Application: By selecting this option, when a user logs on to NetScaler Gateway, it forwards the credentials to the StoreFront website. This setting avoids users from having to enter their credentials twice. However, you must also enable the Pass-through from NetScaler Gateway authentication method on StoreFront. Disable this option if you require users to log on to NetScaler Gateway and the StoreFront store with different credentials.
-
-
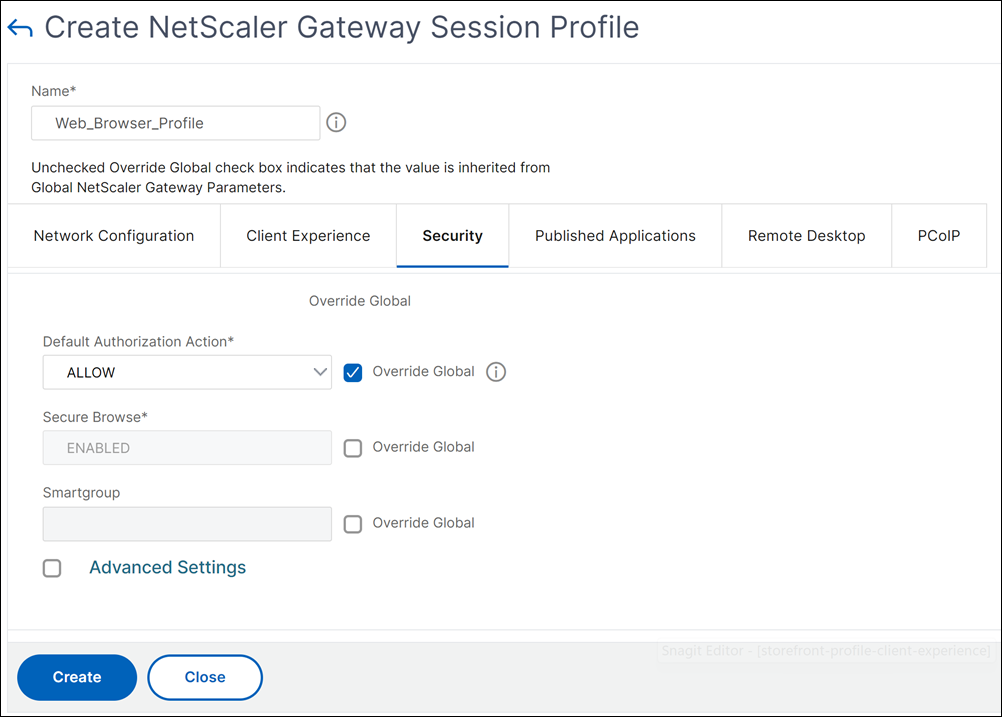
In the Security tab, enable Default Authorization Action and set it to ALLOW.
-
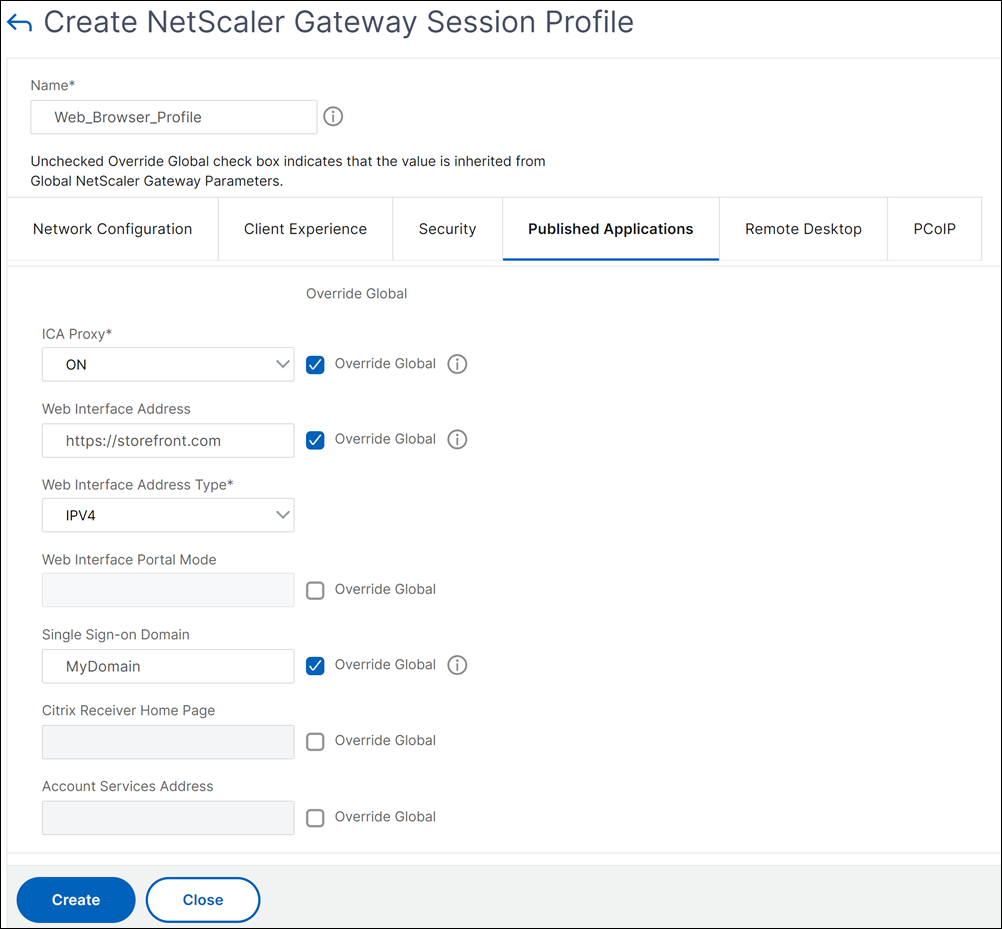
In the Published Applications tab, configure the following settings:
-
ICA Proxy: Set to ON.
-
Web Interface Address: FQDN of the StoreFront™ server followed by the path to the store website.
-
Single Sign-on Domain: If you only use one domain, optionally enter the NetBIOS name for the domain.
-
-
Click Create.
-
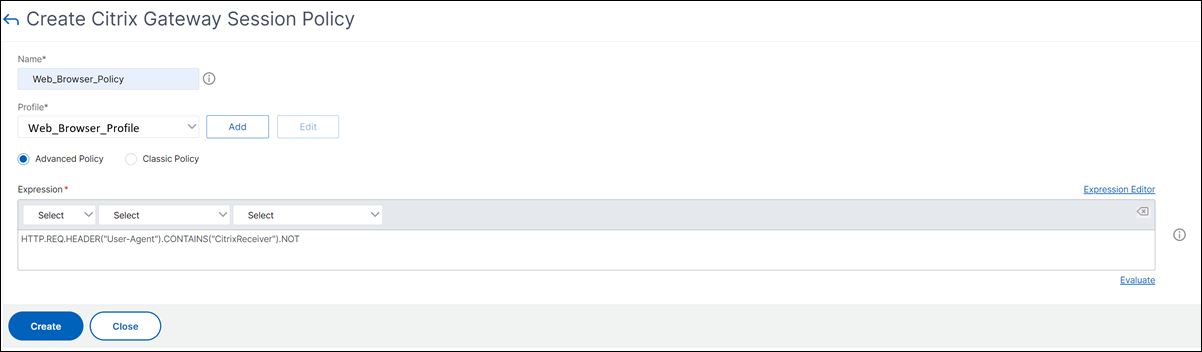
In the Session Policies tab, click Add. The session policy is required for NetScaler to differentiate between the web browser-based and Citrix Workspace app-based connections. This policy is applied to web browser-based connections.
-
In Name, assign a name to session policy.
-
In Profile, select the session profile that you created.
-
Click the Advanced Policy option and enter the following syntax under Expression:
HTTP.REQ.HEADER("User-Agent").CONTAINS("CitrixReceiver").NOT -
Click Create.
For more details about NetScaler Gateway session policies, see Session policies.
2. Create a session policy for Citrix Workspace™ app-based access
-
Navigate to Configuration > NetScaler Gateway > Policies > Session.
-
In the Session Profiles tab, click Add.
-
Assign a name to the session profile for Citrix Workspace app.
-
In the Client Experience tab, enable the following settings:
-
Session Time-out (mins): Set this to the desired inactivity timeout. It is recommended that you select Override Global even if you intend to use the global session timeout settings. Failing to explicitly override this setting, even when using the default 30-minute timeout, can lead to authentication loops and force users to re-login.
-
Plug-in Type: To disable use of the Secure Access client, which is required to establish a full VPN, set this to Java. If you want to allow a full VPN, see Full VPN setup on NetScaler Gateway.
-
Single Sign-on to Web Application: By selecting this option, when a user logs on to NetScaler Gateway, it forwards the credentials to the StoreFront store. If Pass-through from NetScaler Gateway authentication is enabled on StoreFront, this allows single sign-on to the StoreFront store which avoids users from having to enter their credentials twice. Disable this option if you require users to log on to NetScaler Gateway and the StoreFront store with different credentials.
-
-
In the Security tab, enable Default Authorization Action and set it to ALLOW.
-
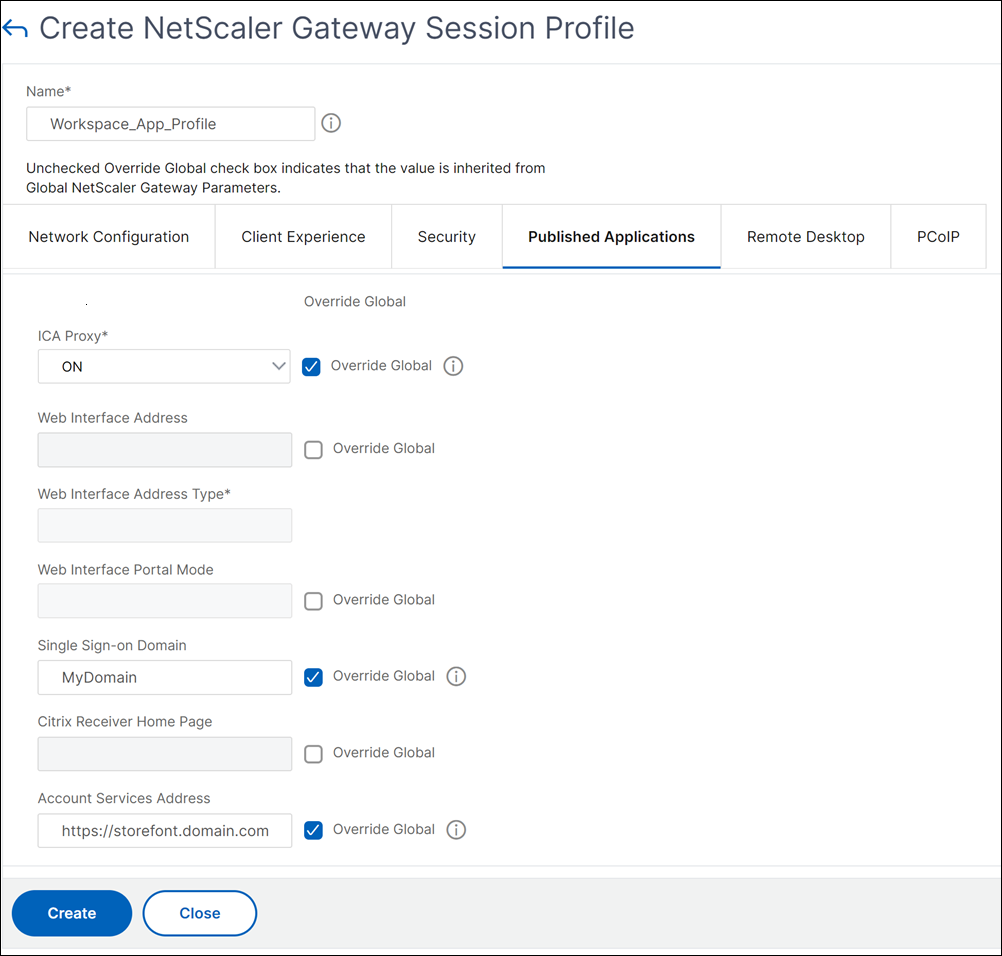
In the Published Applications tab, enable the following settings:
-
ICA Proxy: Set to ON.
-
Account service address: The base URL of the StoreFront™ server or StoreFront server group. Citrix Workspace app uses this address to discover the stores that are available on the server.
-
Single Sign-on Domain: If you only use one domain, optionally enter the NetBIOS name for the domain.
-
-
Click Create.
-
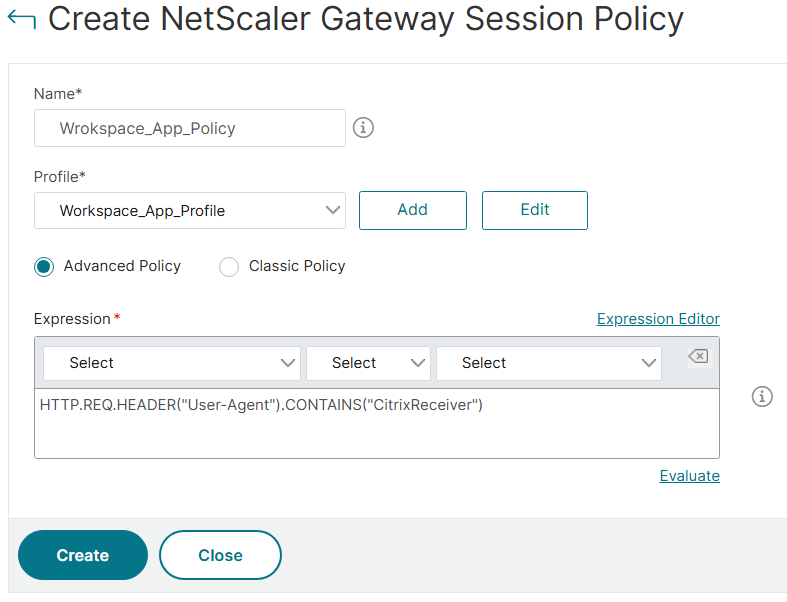
In the Session Policies tab, click Add. The session policy is required for NetScaler to differentiate between the web browser-based and Citrix Workspace app-based connections. This policy is applied to web browser-based connections.
-
In Name, assign a name to session policy.
-
In Profile, select the session profile that you created.
-
Click the Advanced Policy option and enter the following syntax under Expression:
HTTP.REQ.HEADER("User-Agent").CONTAINS("CitrixReceiver") -
Click Create.
3. Create an authentication profile
Create an authentication profile on NetScaler based on the type of authentication method that you need to configure.
Although this step is optional, we recommend it as a good practice to use NetScaler Gateway to authenticate identity of the users before granting access to StoreFront.
Refer to Authentication and Authorization for more details.
4. Create a NetScaler® Gateway virtual server
-
Navigate to NetScaler Gateway > Virtual Servers.
-
Click Add to add a NetScaler Gateway virtual server.
-
Assign a name and IP address to the virtual server.
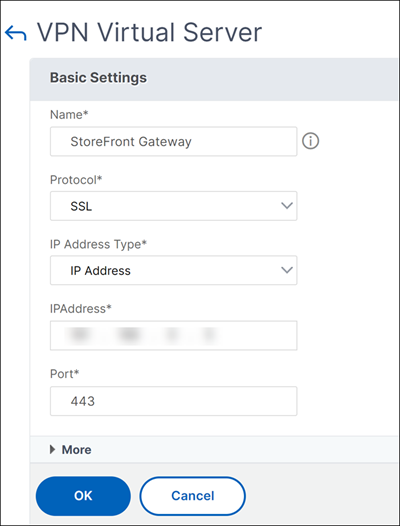 Note:If you choose not to use NetScaler Gateway to authenticate the users, click More and clear the Enable Authentication checkbox.
-
Select OK.
-
Add a certificate.a. Under Certificate, select Server Certificate. b. Upload a server certificate. c. Select Bind.
-
Select Continue.
-
Add the session policies:a. Under Policies, click +. b. From the Choose Policy drop-down list, select Session. From the Type drop-down list, select Request and then click Continue. c. Under Policy Binding, click Select Policy and select the web browser-based session policy and the Citrix Workspace app-based session policy that you previously created and click Bind to bind the session policies to the virtual server.
-
Add the STA servers.a. If the Published Applications section is not displayed then add it from Advanced settings. b. In the Published Applications section, select No STA Server. c. In the STA Server Binding screen, enter the first STA server URL. If you are using Citrix Virtual Apps and Desktops, enter the URLs of the Desktop Delivery Controllers. If you are using Citrix DaaS, enter the URLs of the Citrix Cloud Connectors. d. Select Bind. e. Select 1 STA server. On the VPN Virtual Server STA Server Binding screen, bind further STA servers.Important:Include all STA servers that you configure in StoreFront, otherwise users may experience launch failures.
-
Set the authentication profile.a. If the Authentication Profile section is not displayed then add it from Advanced settings. b. In the Authentication Profile, select the authentication profile you created earlier. c. Select OK.Note:You must choose an authentication profile rather than adding a policy to Basic Authentication. Basic authentication uses classic policies which are no longer supported and may result in log in failures.
-
Set an appropriate UI theme.a. If the Portal Theme section is not displayed then add it from Advanced settings. b. If the StoreFront website is configured with the Classic experience then choose RfWebUI. If the StoreFront website is configured with the Modern experience the choose WStheme. c. Select OK.You can optionally create your own custom theme based on RfWebUI or WStheme.
-
Select Done.
5. Configure StoreFront
For instructions on how to add a NetScaler Gateway to StoreFront, see Configure NetScaler Gateways.