
Deploy NetScaler Gateway in a double-hop DMZ
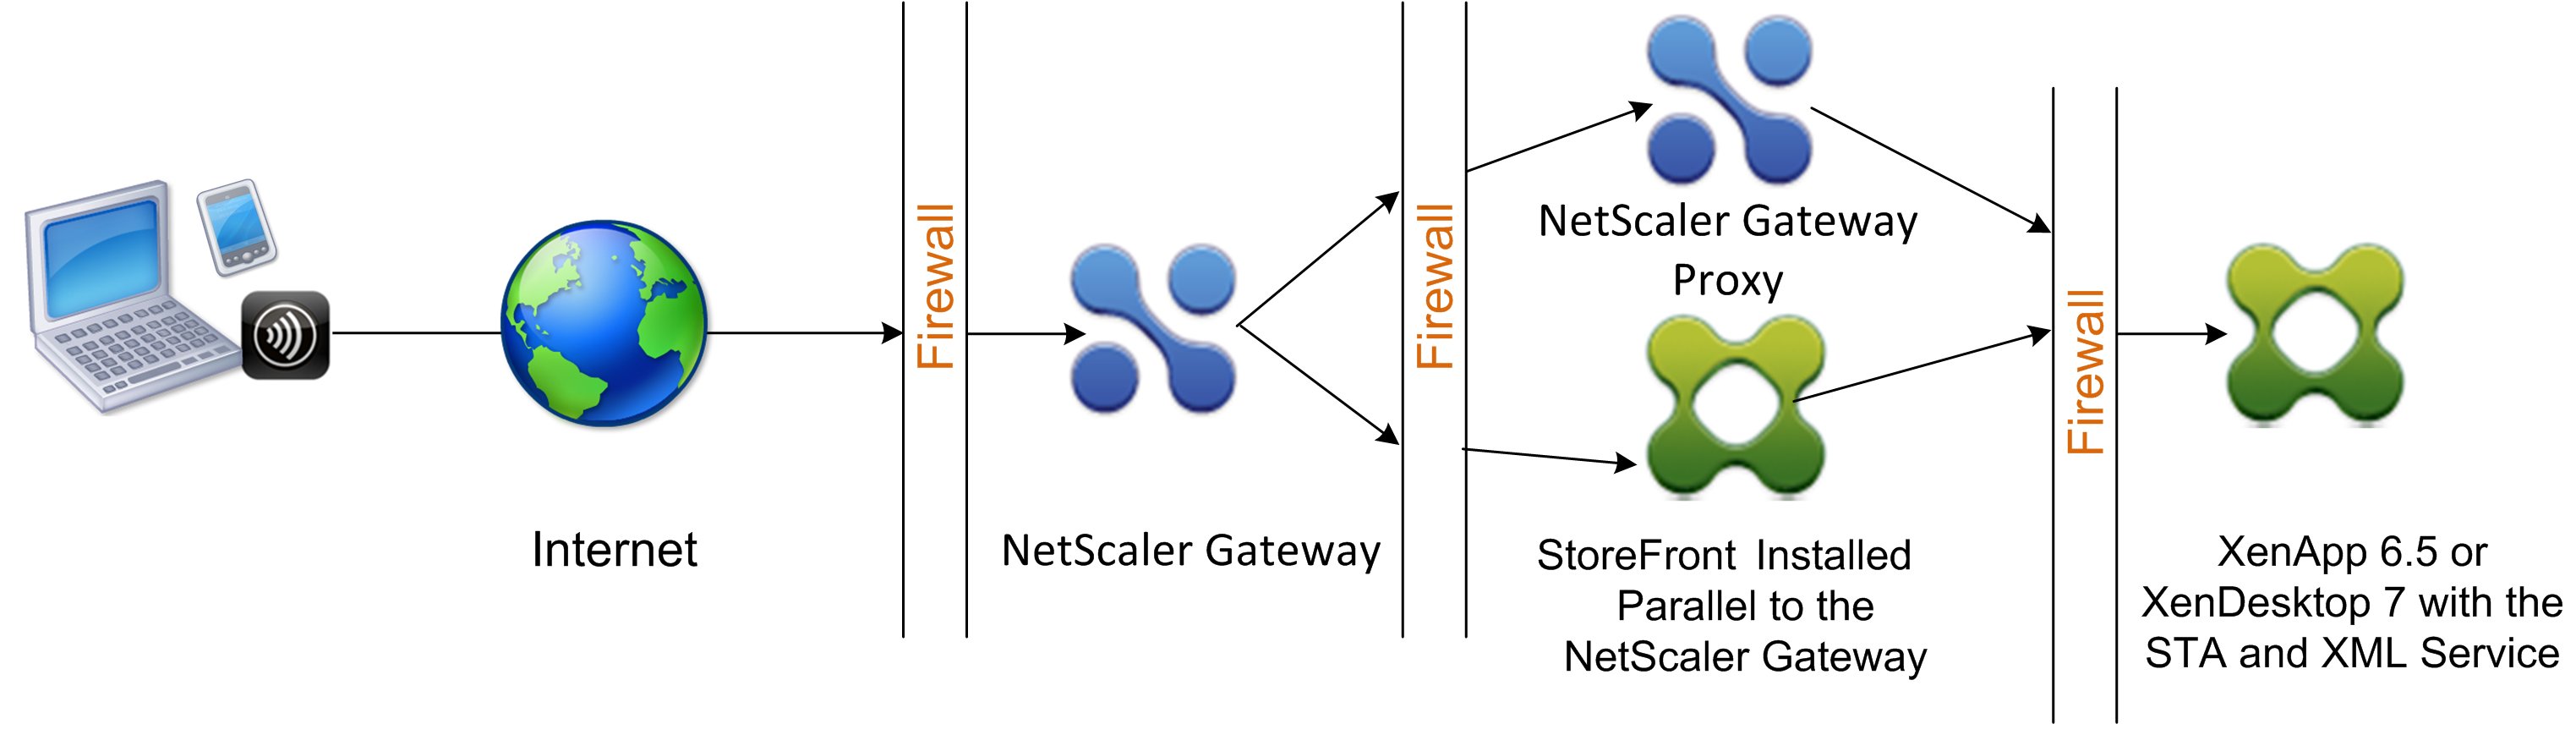
Some organizations use three firewalls to protect their internal networks. The three firewalls divide the DMZ into two stages to provide an extra layer of security for the internal network. This network configuration is called a double-hop DMZ.
Figure 1. NetScaler Gateway appliances deployed in a double-hop DMZ
Note:
For illustration purposes, the preceding example describes a double-hop configuration using three firewalls with StoreFront, NetScaler Gateway, and Citrix Virtual Apps. However, you can also have a double-hop DMZ with one appliance in the DMZ and one appliance in the secure network. If you configure a double-hop configuration with one appliance in the DMZ and one in the secure network, you can ignore the instructions for opening ports on the third firewall.
You can configure a double-hop DMZ to support Citrix StoreFront installed parallel to the NetScaler Gateway proxy. Users connect by using the Citrix Workspace app.
Note:
If you deploy NetScaler Gateway in a double-hop DMZ with StoreFront, email-based AutoDiscovery for Citrix Workspace app does not work.
How a double-Hop deployment works
You can deploy NetScaler Gateway appliances in a double-hop DMZ to control access to servers running Citrix Virtual Apps. The connections in a double-hop deployment occur as follows:
-
Users connect to NetScaler Gateway in the first DMZ by using a web browser and by using the Citrix Workspace app to select a published application.
-
Citrix Workspace app starts on the user device. The user connects to NetScaler Gateway to access the published application running in the server farm in the secure network.Note: Secure Hub and the Citrix Secure Access client for Windows are not supported in a double-hop DMZ deployment. Only the Citrix Workspace app is used for user connections.
-
NetScaler Gateway in the first DMZ handles user connections and performs the security functions of an SSL VPN. This NetScaler Gateway encrypts user connections, determines how the users are authenticated, and controls access to the servers in the internal network.
-
NetScaler Gateway in the second DMZ serves as a NetScaler Gateway proxy device. This NetScaler Gateway enables the ICA traffic to traverse the second DMZ to complete user connections to the server farm. Communications between NetScaler Gateway in the first DMZ and the Secure Ticket Authority (STA) in the internal network are also proxied through NetScaler Gateway in the second DMZ.
NetScaler Gateway supports IPv4 and IPv6 connections. You can use the configuration utility to configure the IPv6 address.
The following table suggests the double-hop deployment support for the various ICA® features:
| ICA feature | Double-hop support |
|---|---|
| SmartAccess | Yes |
| SmartControl | Yes |
| Enlightened Data Transport (EDT) | Yes |
| HDX Insight | Yes |
| ICA Session Reliability (Port 2598) | Yes |
| ICA Session Migration | Yes |
| ICA Session Timeout | Yes |
| Multi-Stream ICA | Yes (TCP only) |
| Framehawk | No |
| UDP audio | No |
Prepare for a double-hop DMZ deployment
When configuring a double-hop DMZ deployment, you must answer the following questions:
-
Do I want to support load balancing?
-
What ports do I open on the firewalls?
-
How many SSL certificates do I need?
-
What components do I need before I begin the deployment?
The topics in this section contain information to help you answer these questions as appropriate for your environment.
Components required to begin the deployment
Before you begin a double-hop DMZ deployment, ensure that you have the following components:
-
At minimum, two NetScaler Gateway appliances must be available (one for each DMZ).
-
Servers running Citrix Virtual Apps™ must be installed and operational in the internal network.
-
StoreFront™ must be installed in the second DMZ and configured to operate with the server farm in the internal network.
-
At minimum, one SSL server certificate must be installed on NetScaler Gateway in the first DMZ. This certificate ensures that the Web browser and user connections to NetScaler Gateway are encrypted.You need extra certificates if you want to encrypt connections that occur among the other components in a double-hop DMZ deployment.